New Post-Quantum Cryptography Standard · AI Agent Security Standard · or both in the Emerging Risks Pack →
Prices in USD · Instant download · Templates in Word and ExcelSupportContact usCart

Shop / Policies & standards

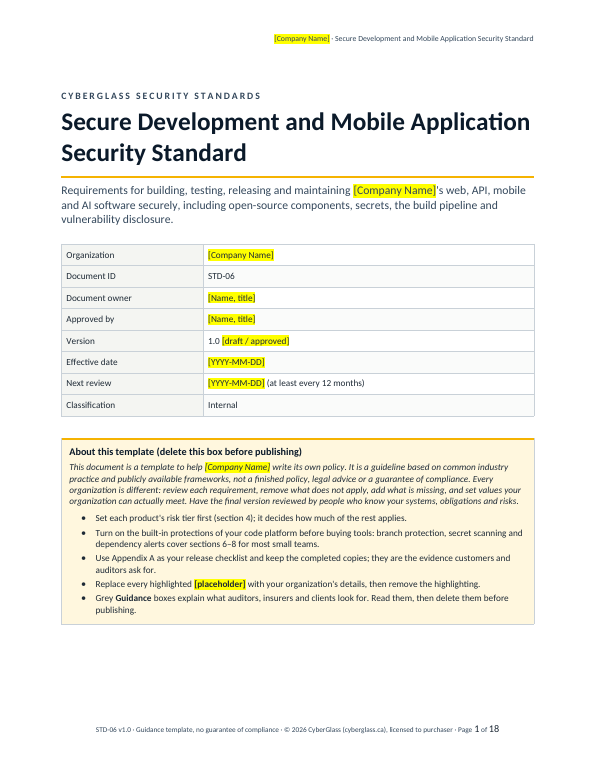
Secure Development and Mobile Application Security Standard

Build web, API, mobile and AI software securely: risk tiers, threat modelling, code review, secrets, open-source and SBOMs, security testing with fix times, mobile app (MASVS) and API controls, and vulnerability disclosure.

First page of the Secure Development and Mobile Application Security Standard

View sample pages (PDF) ↗

What's inside

  • Editable Word standard in formal "shall" language (18 pages)
  • Plain-language explanation of secure development and what customers and investors ask for
  • Three risk tiers so small teams and larger organizations apply the right depth
  • Secure coding, code review, secrets and AI coding assistant rules
  • Open-source and supply chain controls: dependency scanning, SBOM for every release, signed builds
  • Security testing with fix times by severity, plus mobile app (MASVS), API and AI feature requirements
  • Vulnerability disclosure, EU Cyber Resilience Act reporting dates, worked release checklist, measures and definitions

Format

Word (.docx). Editable, with highlighted placeholders and guidance notes you delete before publishing.

Frameworks referenced

  • NIST SP 800-218 (SSDF)
  • OWASP ASVS
  • OWASP MASVS
  • NIST CSF 2.0
  • ISO/IEC 27001:2022

Aligned with the frameworks named. Templates support your program; they don't certify compliance.

Who it's for

Software teams and startups building web, API, mobile or AI products, and security leads answering customer or investor technical due diligence.

Questions

Does it cover mobile apps on both major platforms?

Yes. Section 10 follows the OWASP MASVS control groups, which apply to both major mobile platforms, plus app store privacy disclosures and signing key protection.

Is this a finished standard I can use as is?

No. It's a template: a guideline based on common industry practice. Review each requirement, remove what doesn't apply, set values you can meet, and have the final version reviewed by people who know your systems and obligations.

How do I receive the file?

After checkout you get an instant download link by email from our payment partner.

Refunds and updates

See our licence and refund policy.

Often added

Bundle · Startups
Bundles

Startup Security Bundle

The IT Security Program Kit, Access Management, AI Agent Security and Secure Development standards, plus a 30-day Quick-Start Guide and a Startup Security Tracker.

  • NIST CSF 2.0
  • ISO/IEC 27001:2022
  • SOC 2
US$379Details
New
Policies & standards

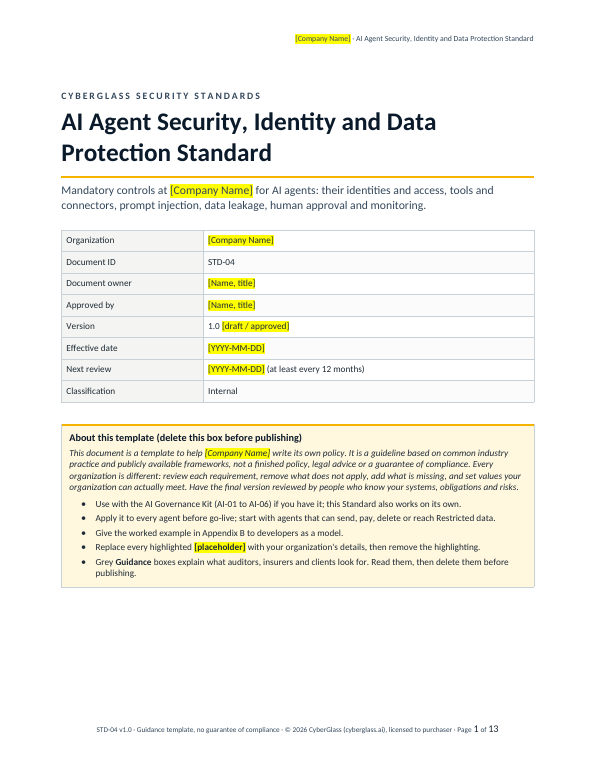
AI Agent Security, Identity and Data Protection Standard

Secure AI agents before they act: own identities and short-lived scoped tokens, tool and tool-server hardening, prompt injection boundaries, data leakage controls and human approval gates.

  • NIST AI RMF 1.0
  • OWASP Top 10 for Agentic Applications
  • NIST CSF 2.0
US$129Details

Use alongside your own licensed copy of the standard. CyberGlass does not sell or reproduce standard text.

Based on NIST CSF 2.0. Republished courtesy of the National Institute of Standards and Technology. NIST does not endorse CyberGlass.