AI Governance Program Kit
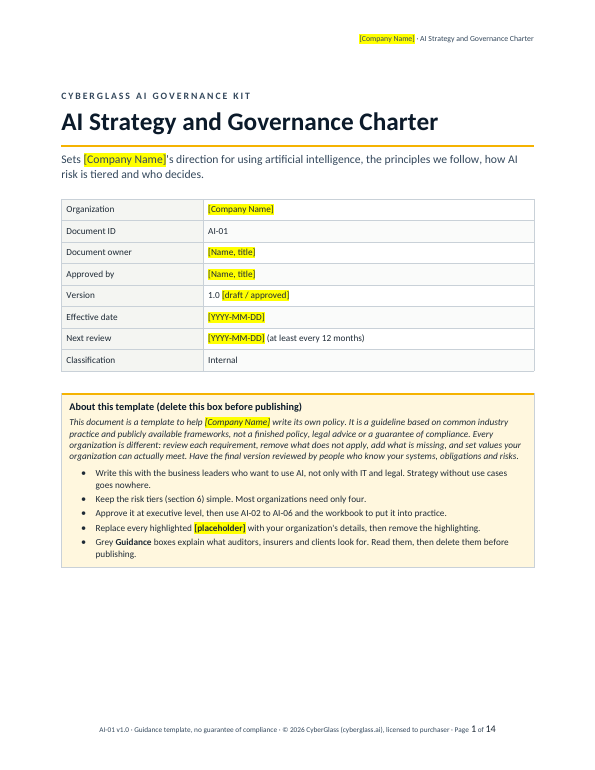
Govern AI use across your organization: strategy, acceptable use, risk and impact assessment, tool approval, AI incidents and a shadow AI review, with a working register.
- NIST AI RMF 1.0
- ISO/IEC 42001:2023
- EU AI Act
Shop / Bundles
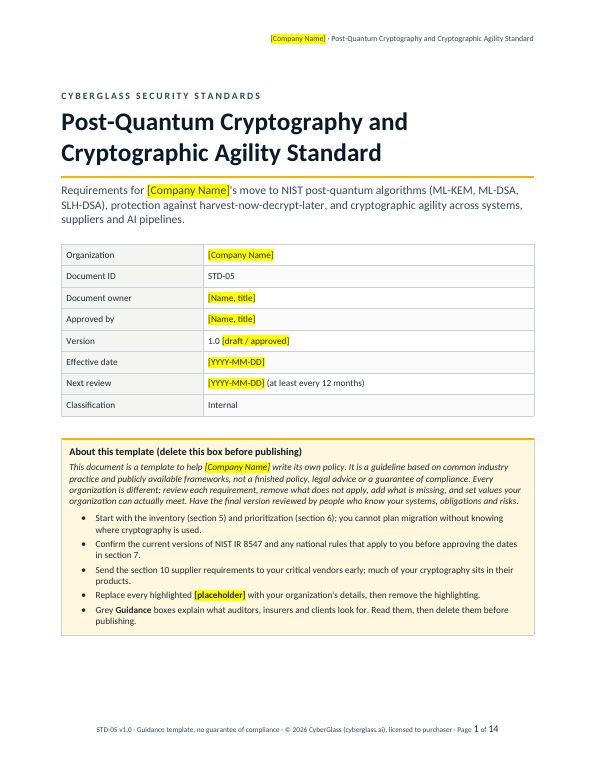
Three standards for the newest risks: help desk impersonation and mass file theft (STD-03), AI agents acting on your systems (STD-04) and the move to post-quantum cryptography (STD-05).
Word (.docx) and Excel (.xlsx). Editable, with highlighted placeholders and guidance notes you delete before publishing.
Aligned with the frameworks named. Templates support your program; they don't certify compliance.
Small and medium organizations, security leads, consultants and MSPs who want a structured starting point instead of a blank page.
No. It's a template: a guideline based on common industry practice. Review each requirement, remove what doesn't apply, set values you can meet, and have the final version reviewed by people who know your systems and obligations.
After checkout you get an instant download link by email from our payment partner.
The licence covers use within your own organization. Consultants and MSPs who want to use templates with clients should contact us.
See our licence and refund policy.
Govern AI use across your organization: strategy, acceptable use, risk and impact assessment, tool approval, AI incidents and a shadow AI review, with a working register.
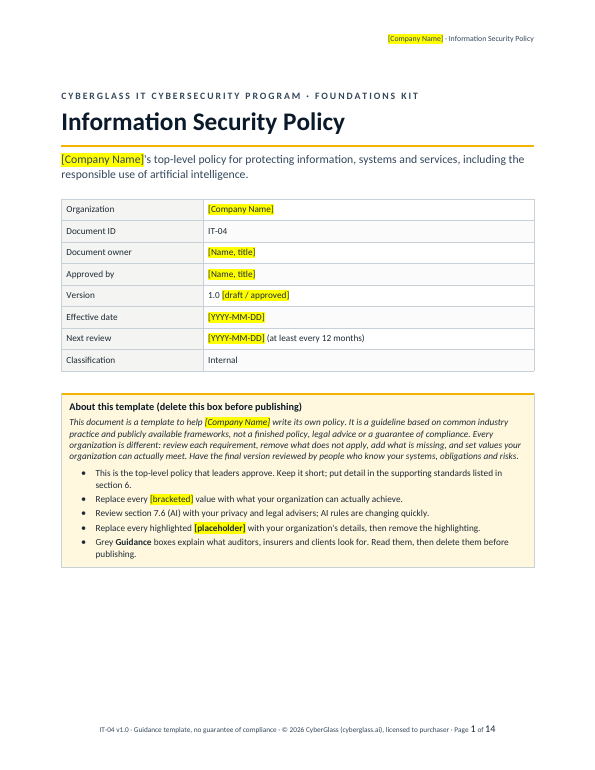
Everything a small or medium business needs to start a cybersecurity program: charter, governance, policy, risk method and registers, ready to edit in Word and Excel.
Use alongside your own licensed copy of the standard. CyberGlass does not sell or reproduce standard text.
Based on NIST CSF 2.0. Republished courtesy of the National Institute of Standards and Technology. NIST does not endorse CyberGlass.