Shop / Bundles
Startup Security Bundle
What AI, SaaS and mobile app startups are asked for by enterprise customers and investors: the IT Security Program Kit, Access Management, AI Agent Security and Secure Development standards, plus a 30-day Quick-Start Guide and a Startup Security Tracker.
What's inside
- START-01 Startup Security Quick-Start Guide: 30-day plan, questionnaire answer map, mobile app security steps (OWASP MASVS), SaaS vendor review, training program, privacy law notes and evidence list (bundle only)
- Startup Security Tracker (Excel): 90-day plan, evidence log with due dates, SaaS vendor register, training log, privacy request log and due-diligence map (bundle only)
- IT Security Program Kit: charter, governance, information security policy, risk method, incident response plan, business continuity and disaster recovery plan, and the IT workbook (risk register, assets, suppliers, vulnerabilities, KPIs, control register)
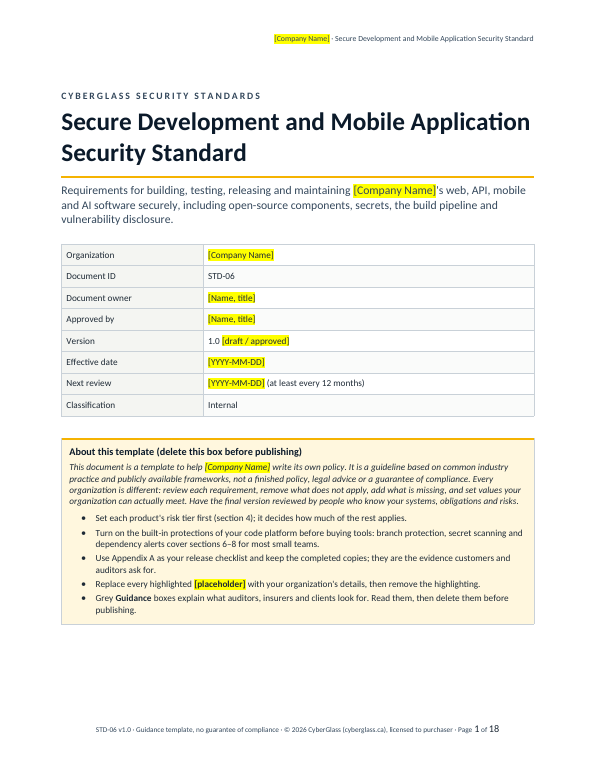
- Access Management Standard (STD-01), AI Agent Security Standard (STD-04), Secure Development and Mobile Application Security Standard (STD-06)
The Quick-Start Guide and Startup Security Tracker are bundle-only extras.
What enterprise reviewers ask, and where you'll find it
| They ask about | Where it's covered |
|---|---|
| Security policy | IT-04 Information Security Policy |
| Access and MFA | STD-01 Access Management Standard |
| Secure development, SBOM, pen testing, fix times | STD-06 sections 4–9 |
| Vendor and SaaS risk | Quick-Start Guide section 5, tracker SaaS Vendors sheet, IT workbook Suppliers sheet |
| Security awareness training | Quick-Start Guide section 4, tracker Training Log |
| Incident response | IT-06 Incident Response Plan |
| Backups and disaster recovery | IT-07 BCDR Plan and BIA workbook |
| AI and AI agents | STD-04 AI Agent Security Standard |
| Privacy | Partly: security and breach response; guide section 7 lists what a privacy program still needs |
| Mobile app data and app-to-API security | STD-06 section 10, Quick-Start Guide section 6 (mobile checklist and MASVS profiles) |
| Evidence auditors sample | Quick-Start Guide section 8, tracker Evidence Log |
Format
Word (.docx) and Excel (.xlsx). Editable, with highlighted placeholders and guidance notes you delete before publishing.
Frameworks referenced
- NIST CSF 2.0
- ISO/IEC 27001:2022
- SOC 2
- NIST SP 800-63B
- NIST AI RMF 1.0
- NIST SP 800-218 (SSDF)
- OWASP MASVS
Aligned with the frameworks named. Templates support your program; they don't certify compliance.
Who it's for
AI, SaaS and mobile app startups preparing for their first enterprise customers, investor due diligence or cyber insurance applications.
Questions
Is this enough for SOC 2?
Not on its own. These documents help you prepare for SOC 2 and ISO/IEC 27001 and answer customer reviews; an independent auditor decides, and you need dated evidence that you follow them.
Does it cover vendor risk, training, backups and privacy?
Vendor reviews, training records and backup and disaster recovery are covered (Quick-Start Guide sections 4–5, the tracker, IT-07 and the IT workbook). Privacy is covered for security and breach response; the guide lists what a privacy program still needs, such as a privacy notice and retention schedule.
How do I receive the files?
After checkout you get an instant download link by email from our payment partner.
Refunds and updates
See our licence and refund policy.
Use alongside your own licensed copy of the standard. CyberGlass does not sell or reproduce standard text.
Based on NIST CSF 2.0. Republished courtesy of the National Institute of Standards and Technology. NIST does not endorse CyberGlass.