New Post-Quantum Cryptography Standard · AI Agent Security Standard · or both in the Emerging Risks Pack →
Prices in USD · Instant download · Templates in Word and ExcelSupportContact usCart

Shop / Program kits

AI Governance Program Kit

Govern AI use across your organization: strategy, acceptable use, risk and impact assessment, tool approval, AI incidents and a shadow AI review, with a working register.

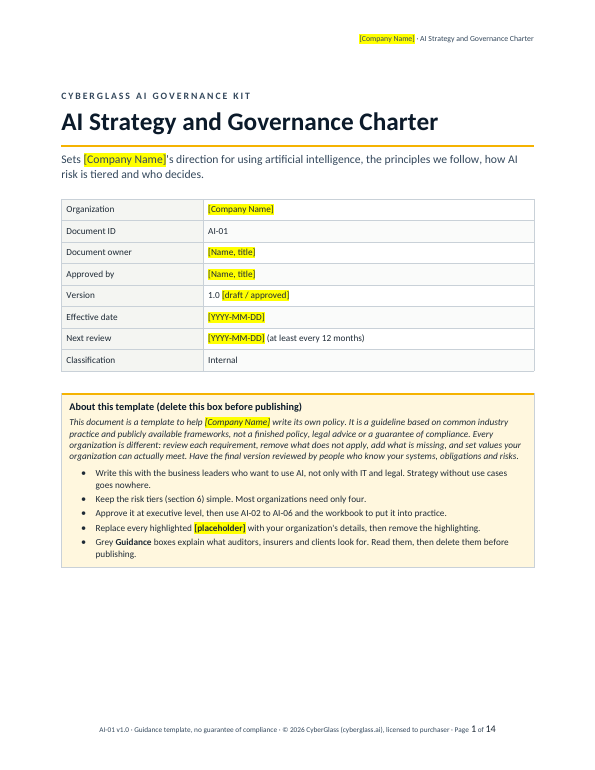
First page of AI Governance Program Kit

View sample pages (PDF) ↗

What's inside

  • 00 Master Implementation Roadmap: a 24-week plan in five phases mapped to the NIST CSF 2.0 functions, telling you which document to use when, plus a CSF 2.0 Cross-Mapping Matrix showing which documents address each of the 106 outcomes
  • AI Strategy and Governance Charter: vision, principles, use-case strategy, risk tiers, AI Governance Committee, decision rights and a 12-month roadmap
  • AI Acceptable Use Policy: approved tools, data rules, prohibited uses, human review, disclosure, meeting assistants and AI agents
  • AI Risk and Impact Assessment Method: tiering questions, risk categories, impact on people, testing and a worked example
  • AI Tool Approval and Vendor Assessment: intake workflow, request form, 22-question vendor questionnaire with scoring and a contract checklist
  • AI Incident Response Playbook: six playbooks including prompt injection, data entered into the wrong tool and deepfake fraud
  • Shadow AI Baseline Review Guide: discovery sources, staff survey, decisions and control testing
  • Excel workbook: AI inventory, AI risk register, tool requests, vendor scoring, shadow AI findings, framework gap sheet (NIST AI RMF, ISO/IEC 42001, EU AI Act) and self-calculating KPIs
  • Every document now includes real-world incidents, Auditor Red Flag callouts, small-business vs enterprise notes, worked examples, and a Control Register in the workbook that links each control ID to its owner and evidence
  • Links 38 of 106 NIST CSF 2.0 outcomes to specific sections, shown in the CSF 2.0 Cross-Mapping Matrix
  • Not included: training slide decks. The documents set the training requirements; deliver them with your own provider or materials

Format

Word (.docx) and Excel (.xlsx). Editable, with highlighted placeholders and guidance notes you delete before publishing.

Frameworks referenced

  • NIST AI RMF 1.0
  • ISO/IEC 42001:2023
  • EU AI Act
  • NIST CSF 2.0
  • ISO/IEC 27001:2022

Aligned with the frameworks named. Templates support your program; they don't certify compliance.

Who it's for

Small and medium organizations, security leads, consultants and MSPs who want a structured starting point instead of a blank page.

Questions

Is this a finished policy I can use as is?

No. It's a template: a guideline based on common industry practice. Review each requirement, remove what doesn't apply, set values you can meet, and have the final version reviewed by people who know your systems and obligations.

How do I receive the files?

After checkout you get an instant download link by email from our payment partner.

Can I share it with clients?

The licence covers use within your own organization. Consultants and MSPs who want to use templates with clients should contact us.

Refunds and updates

See our licence and refund policy.

Often added

New
Policies & standards

AI Agent Security, Identity and Data Protection Standard

Secure AI agents before they act: own identities and short-lived scoped tokens, tool and tool-server hardening, prompt injection boundaries, data leakage controls and human approval gates.

  • NIST AI RMF 1.0
  • OWASP Top 10 for Agentic Applications
  • NIST CSF 2.0
US$129Details
New
Bundles

Emerging Risks Pack: Identity, AI Agents and Post-Quantum

Three standards for the newest risks: help desk impersonation and mass file theft (STD-03), AI agents acting on your systems (STD-04) and the move to post-quantum cryptography (STD-05).

  • NIST SP 800-63B
  • NIST AI RMF 1.0
  • OWASP Top 10 for Agentic Applications
US$249Details

Use alongside your own licensed copy of the standard. CyberGlass does not sell or reproduce standard text.

Based on NIST CSF 2.0. Republished courtesy of the National Institute of Standards and Technology. NIST does not endorse CyberGlass.