Shop / Single templates
Risk Management Methodology
A single editable IT document you can adapt to your organization and put to work quickly.
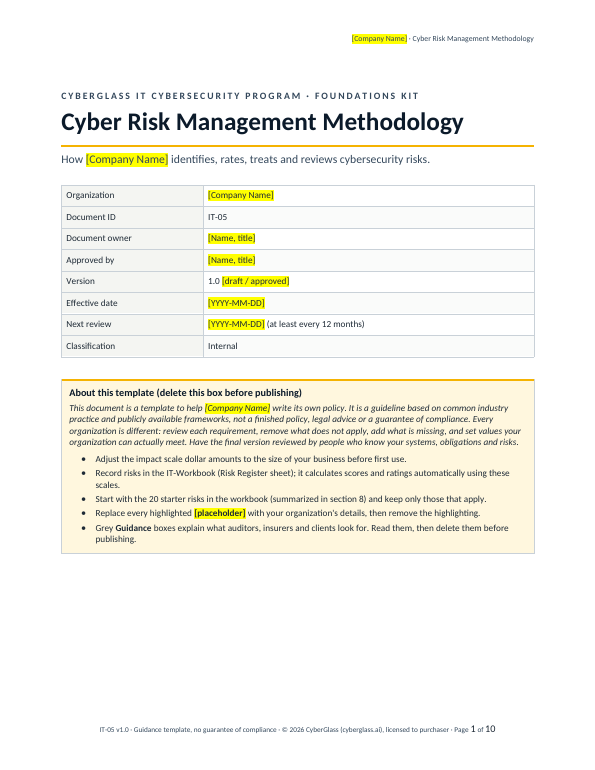
What's inside
- Editable Word document (.docx)
- Guidance notes explaining what auditors, insurers and clients look for
- Framework mapping and references
Format
Word (.docx). Editable, with highlighted placeholders and guidance notes you delete before publishing.
Frameworks referenced
- Cyber Centre baseline
- ISO/IEC 27001:2022
- NIST CSF 2.0
- Privacy laws (GDPR, PIPEDA)
- SOC 2
Aligned with the frameworks named. Templates support your program; they don't certify compliance.
Who it's for
Small and medium organizations, security leads, consultants and MSPs who want a structured starting point instead of a blank page.
Questions
Is this a finished policy I can use as is?
No. It's a template: a guideline based on common industry practice. Review each requirement, remove what doesn't apply, set values you can meet, and have the final version reviewed by people who know your systems and obligations.
How do I receive the files?
After checkout you get an instant download link by email from our payment partner.
Can I share it with clients?
The licence covers use within your own organization. Consultants and MSPs who want to use templates with clients should contact us.
Refunds and updates
See our licence and refund policy.
Use alongside your own licensed copy of the standard. CyberGlass does not sell or reproduce standard text.
Based on NIST CSF 2.0. Republished courtesy of the National Institute of Standards and Technology. NIST does not endorse CyberGlass.